2,24 millones de hosts PHP orientados a Internet, 59% en versiones sin corrección: lo que sabemos sobre php2shell
Tabla de contenido
PHP lanzó una versión de seguridad de emergencia el 21 de octubre de 2026, aproximadamente a las 13:35 UTC, unos 25 minutos antes del horario previsto, por dos vulnerabilidades críticas en el núcleo de PHP, CVE-2026-109618 y CVE-2026-109619, ambas clasificadas como 9.2 según el CVSS v4.0. PHP ahora confirma que pueden permitir la ejecución remota de código sin autenticación, y los investigadores los llaman “php2shell”, un nombre que implica que un atacante podría obtener un shell en un servidor vulnerable. Las versiones estables son PHP 8.5.12, 8.4.27, 8.3.36 y 8.2.35.
El incidente comenzó con un filtración. La mañana del 20 de octubre, un post de Hacker News que ya se ha eliminado afirmaba que las dos vulnerabilidades estaban a punto de ser reveladas; en cuestión de horas, watchTowr confirmó que eran reales y dijo que había reproducido el CVE-2026-109618. Luego, el equipo de seguridad de PHP programó su lanzamiento un día antes del embargo original, y finalmente lo lanzó antes del nuevo plazo.
El alcance de PHP es lo que aporta valor: potencia sitios web de WordPress, Drupal, Joomla y Magento, plataformas de alojamiento compartido, paneles de control y una gran cantidad de software de terceros. No lo anuncia. Los ataques comenzaron antes del parche: a las 07:43 UTC., El CTO de Cloudflare informó sobre el surgimiento de ataques iniciales, y Aikido También ha informado sobre la explotación en estado salvaje. Sansec había advertido de la explotación masiva en el interior de 15 minutos del lanzamiento.
La solución se realiza a nivel de infraestructura: la actualización de PHP en el servidor es la única solución oficial, y las actualizaciones de CMS o plugins no aplicarán dicha actualización..
A Free PHP Check is available Aquí.
Paste your domains, see which sites still run a PHP version exposed to php2shell, ranked by what to patch first.
Cronología
La información fue inicialmente mantenida en secreto hasta el jueves 22 de octubre a las 11:00 ET; tras la filtración, PHP programó su publicación para el 21 de octubre a las 14:00 UTC, Luego lo enviaron unos 25 minutos antes del horario previsto..
Puede revisar la cronología técnica de manera más detallada a continuación..
| Fecha (UTC) | Evento | Fuente |
|---|---|---|
| 21 de octubre, 13:35 | PHP lanza las versiones 8.5.12, 8.4.27, 8.3.36 y 8.2.35, aproximadamente 25 minutos antes del horario previsto, con parches mínimos de código fuente para PHP 7.4, 8.0 y 8.1. | Help Net Security |
| 21 de octubre, 09:18 | Aikido reporta casos de explotación en la naturaleza, citando a Cloudflare | Aikido |
| 21 de octubre, 07:43 | El CTO de Cloudflare reporta ataques iniciales; las reglas de WAF de Cloudflare se amplían a todos los planes, incluido el gratuito | Mattias Geniar |
| 21 de octubre | Cloudflare publica una actualización de emergencia a su conjunto de reglas WAF gestionadas, añadiendo cuatro reglas que se cree que tienen como objetivo estas vulnerabilidades (su registro de cambios no menciona PHP). | El repositorio |
| 21 de octubre | Un sitio que afirma publicar código de exploits en funcionamiento se hace público; se informa que los hosts de WordPress empiezan a desactivarlo session.upload_progress | El repositorio |
| 20 de octubre | CERT-EU publica la Nota de Seguridad 2026-018 | CERT-EU |
| 20 de octubre | PHP security team posts advance notice: two critical vulnerabilities, both CVSS v4.0 9.2 | CERT-EU |
| 20 de octubre | watchTowr confirms the leaked vulnerabilities are real and names CVE-2026-109618 and CVE-2026-109619 | El repositorio |
| 20 de octubre | A Hacker News post, since removed, reports two upcoming PHP RCE disclosures, breaking the embargo | El repositorio |
Lo que sabemos sobre las vulnerabilidades
PHP has now published the fix and its advisory; some details still come only from researchers and should be treated as provisional.
Confirmado por PHP
- Impacto: PHP’s release announcement describes two critical vulnerabilities that can allow unauthenticated remote code execution, and now names CVE-2026-109618 and CVE-2026-109619 itself.
- Component: the PHP changelog lists both fixes under Core, as two GitHub security advisories that avoid state corruption via “bailout”, a mechanism inside the interpreter itself. Researchers, including Mattias Geniar, link the confirmed attack paths to session upload progress and multipart request parsing, both enabled by default.
- Nature: CVE-2026-109619 is described as remote code execution via stale global state: internal state that survives after the memory behind it has been freed.
- Mitigación: PHP states that there are no complete mitigations and updating is the only safe choice.
- Scope: every PHP installation that serves web requests is affected, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed, and the PHP team reports finding the flaws in every PHP version since PHP 5.
Reportado, no confirmado por PHP
- Exploitation at scale: Cloudflare y Aikido report attacks in the wild.
- Public exploit code: proof-of-concept code is circulating. Before the release, Tenable could not verify that any of it worked; since then, Help Net Security reports that a working exploit has shown a single unauthenticated request can trigger the attack.
- Nature: before the release, GMO Flatt Security read a researcher’s demo video, labelled “php2shell”, as showing a memory corruption bug, reproduced on mod_php and PHP-FPM and on WordPress, Laravel and Symfony setups.
Versiones afectadas y estado de los parches
Only the four supported branches, PHP 8.2 to 8.5, received official releases. For PHP 7.4, 8.0 and 8.1, the PHP security team published minimal source backports, but these are meant for people who build PHP themselves and are not something a hosting account can apply. PHP publishes nothing for older branches, although some distributions and LTS vendors may backport fixes.
| PHP branch | Support status | Fix |
|---|---|---|
| 8.5 | Active support | 8.5.12 |
| 8.4 | Active support | 8.4.27 |
| 8.3 | Security fixes only | 8.3.36 |
| 8.2 | Security fixes only, until 31 Dec 2026 | 8.2.35 |
| 7.4, 8.0, 8.1 | End of life | No official release; minimal source patches only |
| 7.3 and older | End of life | None from PHP |
Being on a supported branch is not enough on its own: the server must run the new patch level, and Linux distributions that package PHP may ship the fix under their own version numbers, so check your vendor’s advisory. Support dates are based on the php.net supported versions timetable, as reported by mySites.guru.
Exposición: ¿Cuántos activos y dónde?
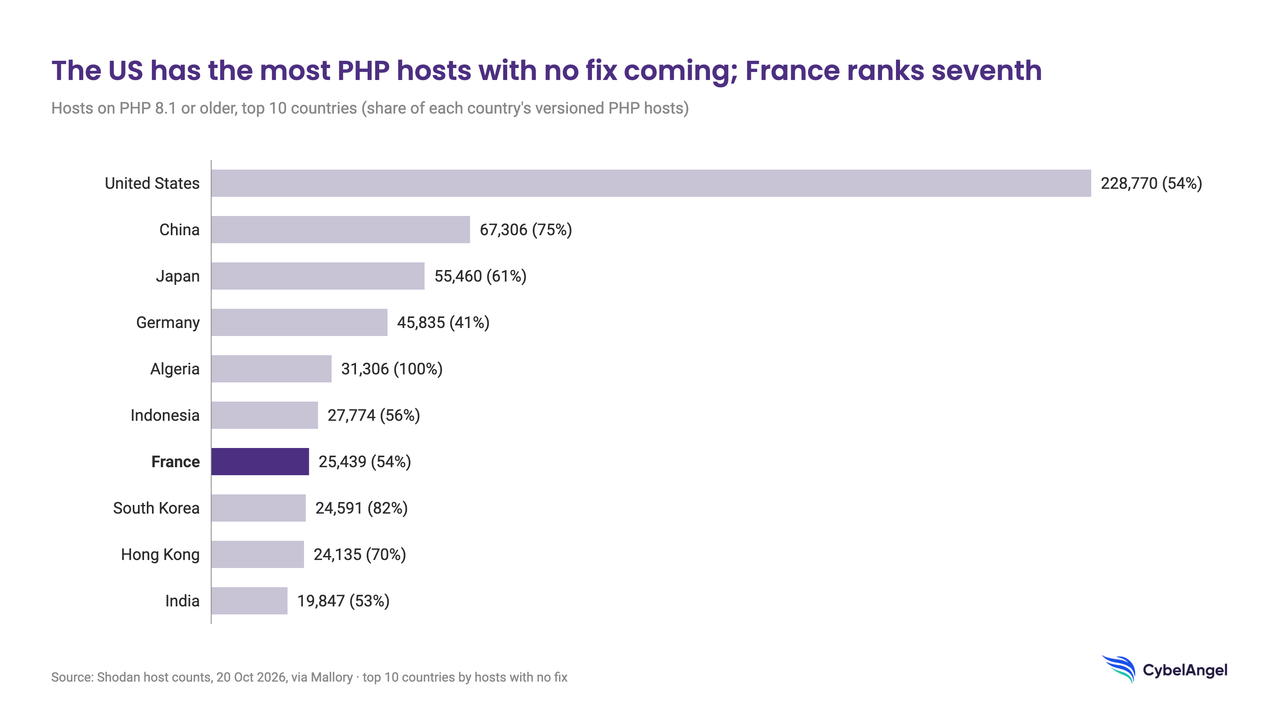
About 2.24 million internet-facing hosts advertise PHP, and 59% of those that report a version (883,717 of about 1.5 million) run a branch with no official release. These figures come from Shodan banner counts published by Mallory on 20 October 2026; they count hosts, not organisations or websites.
Por versión
PHP 8.2 to 8.5 account for 612,269 versioned hosts and are covered by the official release. PHP 5.x (368,570), 7.x (329,358) and 8.0–8.1 (185,789) are not; only some of the 7.x, 8.0 and 8.1 hosts can benefit from PHP’s source patches, if their operators build PHP themselves. PHP 5.6 and 7.2 alone represent about 371,000 hosts for which PHP publishes no fix at all.
Por país
The United States has the largest number of hosts with no official release (228,770), followed by China, Japan and Germany. Among these ten countries, Algeria (100%, almost entirely PHP 5.3 on Telecom Algeria), South Korea (82%) and China (75%) have the highest shares. France counts 25,439 such hosts, 54% of its versioned PHP hosts.
Por el proveedor de alojamiento
Exposure is concentrated: Amazon (293,480 PHP hosts), Hostinger (142,401) and Alibaba Cloud (81,078) host the largest PHP populations, which makes provider-side patching decisive.
WordPress
Según WordPress.org statistics reported by The Repository, 35.1% of WordPress sites run a PHP version the PHP project no longer supports, including 16.46% on PHP 7.4. Across the live Joomla and WordPress sites mySites.guru monitors, 22.7% run PHP 8.1 or older.
Limitaciones de estos números
The real exposure is higher than banner counts suggest: about 740,000 PHP hosts hide their version, and shared hosting puts many websites behind one IP. Conversely, some Linux distributions (Debian, Ubuntu, RHEL) and LTS vendors backport fixes to older packages, so some hosts that report an old version may already be patched.
Un conteo diferente coloca a Francia en primer lugar
Measuring active PHP services rather than hosts, Infrawatch observes about 11 million services across 4.38 million IP addresses, with France at 6.62 million, more than eight times the United States. Much of that concentration comes from Freebox OS, the management software of Free’s home routers; Infrawatch stresses this does not mean these hosts are exploitable.
Recomendaciones
The fix is out: patch PHP itself now; every other measure only buys time.
- Inventory every internet-facing PHP asset, including those run by hosting providers, agencies and appliance vendors, and record the branch and SAPI (PHP-FPM, mod_php, php-cgi).
- Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35, then restart PHP-FPM or the web server so the new interpreter is loaded. Check the version the site reports while serving a request, not
php -v, as the two binaries often differ. - On managed hosting, confirm with your host that the patch is applied, and take a fresh backup before anything changes on the server.
- Upgrade end-of-life branches (8.1 and older) to a supported version, or ask your distribution or LTS vendor for a backported fix. Until then, restrict access (VPN, IP allowlist) or isolate internet-facing applications, as CERT-EU recommends.
- Reduce exposure until you patch: take internet-facing PHP applications offline where you can.
- Check for compromise after patching, going back to at least June 2026: web shells, unexpected or modified PHP files, new admin users and unusual outbound connections. Watch for unexpected child processes of the web server, reduce the data and cloud privileges held by PHP servers, and check that logs are retained.
Cómo CybelAngel está ayudando
Our teams are reviewing the external perimeters we monitor for the signals that matter here: exposed web servers, outdated software stacks and PHP-based control panels. Where we see heightened risk, we are reaching out to customers directly. If you are not a CybelAngel customer and want to understand your external exposure, contact our team.
Updated on 21 October 2026 after PHP’s security release. We will keep updating this article as exploitation data and vendor advisories emerge.
Sobre el autor