2.24万台のPHPホストがインターネットに接続されており、59% 台は修正がないバージョンです:php2shellについて知っておくべきこと
目次
PHP は 2026 年 10 月 21 日の UTC 時間 13:35 に緊急セキュリティリリースをリリースしました。これは予定より約 25 分早く、PHP コアの 2 つの重大脆弱性である CVE-2026-109618 および CVE-2026-109619 に対応したもので、どちらも CVSS v4.0 で 9.2 の評価を受けました。 PHP は現在 認証されていないリモートコード実行を許可できることを確認します, そして研究者らはこれを「php2shell」と呼んでいます。この名称は、攻撃者が脆弱なサーバー上でシェルを取得できることを示しています。既定のバージョンは PHP 8.5.12、8.4.27、8.3.36、および 8.2.35.
この事件は以下のような形で始まった。 漏洩. 10月20日の朝、削除されたハッカーニュースの投稿では、この2つの脆弱性が公開される寸前だと主張されていた。数時間後、watchTowrはそれらが実在であることを確認し、CVE-2026-109618を再現したと述べた。その後、PHPのセキュリティチームは、元の封印よりも1日早くリリースを予定し、結局はその新しい締め切りより前にリリースした。.
このリスクは PHP の普及から生じます。PHP は WordPress、Drupal、Joomla、Magento のサイト、共有ホスティングプラットフォーム、管理パネル、そして多くのベンダー製のソフトウェアをサポートしています。 宣伝していない. 攻撃はパッチ適用前の時間、07:43 UTCに開始されました。, CloudflareのCTOは、初期の攻撃の発生を報告した, 、そして 合気道 野生での搾取も報告されています。サンセックは、大規模な搾取が起こる可能性があると警告していました。 リリースから15分.
修正はインフラレベルで行われます。サーバー側のPHPのアップデートが唯一の正式な対策であり、CMSやプラグインのアップデートではその対策は適用されません。.
無料のPHPチェックが利用可能です こちら.
ドメインを貼り付け、どのサイトがまだ php2shell に公開されている PHP バージョンを実行しているかを確認します。まずパッチすべき項目を順に並べます。.
タイムライン
この情報公開は当初、10月22日木曜日の11:00 ETまで機密扱いとなっていましたが、リーク後にPHPは10月21日14:00 UTCに公開を予定しました。, その後、約25分早く発送しました。.
技術的な経過をより詳細に確認するには、以下をご覧ください。.
| 日付(UTC) | イベント | ソース |
|---|---|---|
| 10月21日、13:35 | PHP は 8.5.12、8.4.27、8.3.36、および 8.2.35 をリリースしました。これは予定より約 25 分早く、PHP 7.4、8.0、および 8.1 用のソースパッチは最小限にとどめました。 | ヘルプネットセキュリティ |
| 10月21日、午前9時18分 | AikidoはCloudflareを引用して野生での搾取を報告している | 合気道 |
| 10月21日、午前7時43分 | CloudflareのCTOが初期の攻撃を報告;CloudflareのWAFルールがすべてのプランに拡大、無料プランも含む | マティアス・ジェニアー |
| 10月21日 | CloudflareはマネージドWAFルールセットに緊急アップデートをリリースし、これら脆弱性を狙った4つのルールを追加した(その変更ログにはPHPは記載されていない)。 | リポジトリ |
| 10月21日 | 動作確認済みのエクスプロイトコードを公開すると主張するサイトが公開され、報告によるとWordPressのホスト企業がその機能を無効にしている。 session.upload_progress | リポジトリ |
| 10月20日 | CERT-EUがセキュリティアドバイザリ 2026-018を発行 | CERT-EU |
| 10月20日 | PHP セキュリティチームが事前通知:2 つの重大脆弱性、どちらも CVSS v4.0 9.2 | CERT-EU |
| 10月20日 | watchTowrは、リークされた脆弱性が実在することを確認し、CVE-2026-109618とCVE-2026-109619という脆弱性を特定した。 | リポジトリ |
| 10月20日 | 削除されたHacker Newsの記事によると、今後2つのPHP RCEの暴露が予定されており、これによって封印が破られる。 | リポジトリ |
脆弱性について知っていること
PHPは現在、修正とアドバイザリーを公開しました。一部の詳細情報はまだ研究者からのみ得られており、暫定的なものとして扱われるべきです。.
PHPによる確認済み
- 影響PHP のリリース発表文の記述 認証されていないリモートコード実行を可能にする2つの重大な脆弱性, そして、現在は CVE-2026-109618 と CVE-2026-109619 という名前が使われています。.
- コンポーネントPHP の changelog には、Core の修正と、GitHub のセキュリティ勧告の 2 つがリストされています。 「救済策」による国家の腐敗を避ける“, インタープリタそのものの内部にある仕組みです。研究者を含め、 マティアス・ジェニアー, 既定で有効になっている確認された攻撃経路をセッションのアップロードの進行状況とマルチパートリクエストの解析とリンクします。.
- 自然CVE-2026-109619 は、リモートでのコード実行として記述されています。 恒久的なグローバルな状態: 記憶装置のメモリが解放された後に残る内部状態。.
- 緩和PHPでは、 完全な対策はありません。アップデートが唯一の安全な選択です。.
- 対象範囲ウェブリクエストを処理するすべての PHP インストールに影響があります。, PHP-FPM、Mod_phpを備えた Apache、php-cgi、FrankenPHP、および LiteSpeed を含む, そして、PHPチームはその欠陥を発見したと報告しています。 PHP 5 以降のすべての PHP バージョン.
報告されたもので、PHPでは確認されていません。
- 大規模な搾取: Cloudflare と 合気道 野生での攻撃を報告する。.
- 公開的な悪用コードコンセプト・コードが公開されています。リリース前に、, Tenableは確認できなかった。 それらのどれかが実を結んだこと;それ以来、, ヘルプネットセキュリティの報告 作業用エクスプロイトにより、認証されていない単一のリクエストが攻撃を引き起こすことが示された。.
- 自然発売前、, GMOフラットセキュリティ 「php2shell」とラベル付けされた研究者のデモ動画を読み、それはモディップとPHP-FPM、そしてWordPress、Laravel、Symfonyのセットアップで再現されるメモリ破損のバグを示していると判断した。.
影響を受けるバージョンとパッチのステータス
サポートされている4つのバージョン(PHP 8.2~8.5)のみが正式なリリースを受けました。PHP 7.4、8.0および8.1については、PHP セキュリティチームが公開しました。 最小限のソースバックポート, ですが、これらは自分で PHP を構築する人向けです。 ホスティングアカウントで適用できるものではありません. PHP は古いブランチに対して何も公開していません。ただし、一部のディストリビューションや LTS バイヤーは修正をバックポートする場合があります。.
| PHPブランチ | サポートステータス | 修正 |
|---|---|---|
| 8.5 | 積極的なサポート | 8.5.12 |
| 8.4 | 積極的なサポート | 8.4.27 |
| 8.3 | セキュリティ修正のみ | 8.3.36 |
| 8.2 | セキュリティ修正のみ対応、2026年12月31日まで | 8.2.35 |
| 7.4, 8.0, 8.1 | End of life | No official release; minimal source patches only |
| 7.3 and older | End of life | None from PHP |
Being on a supported branch is not enough on its own: the server must run the new patch level, and Linux distributions that package PHP may ship the fix under their own version numbers, so check your vendor’s advisory. Support dates are based on the php.net supported versions timetable, as reported by mySites.guru.
エクスポージャー:どのくらいの資産、どこに
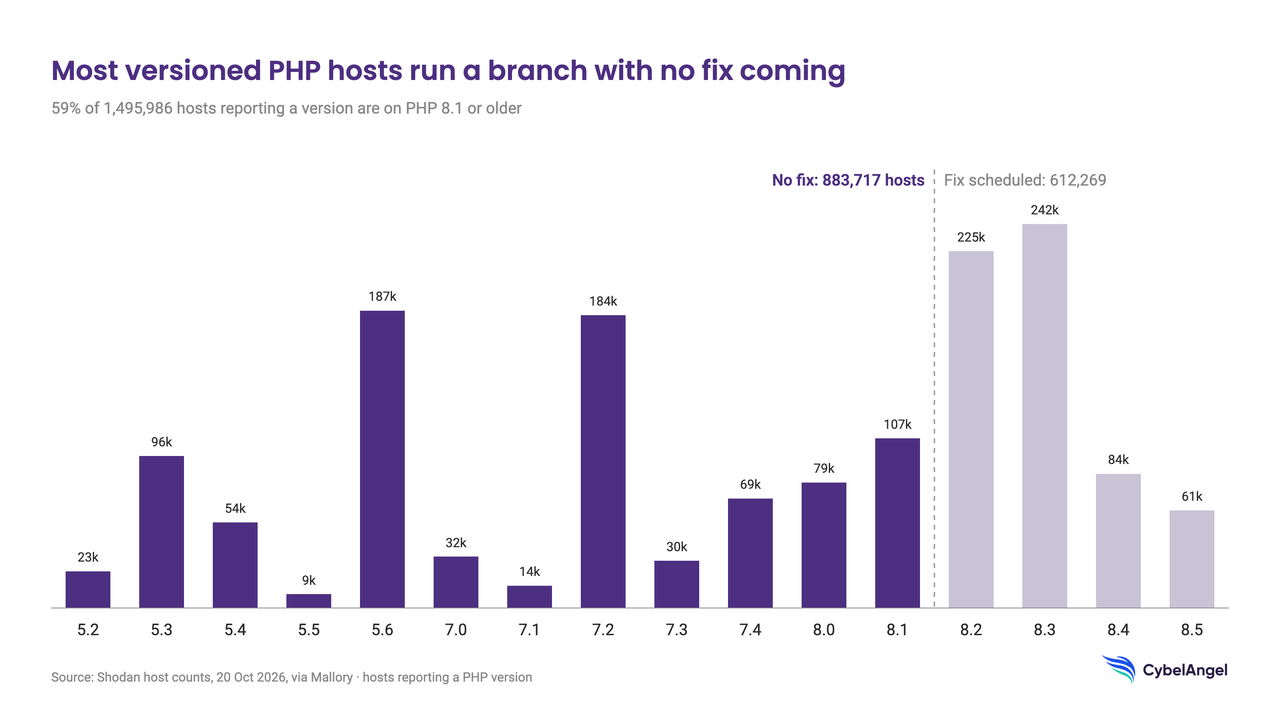
About 2.24 million internet-facing hosts advertise PHP, and 59% of those that report a version (883,717 of about 1.5 million) run a branch with no official release. These figures come from Shodan banner counts published by Mallory on 20 October 2026; they count hosts, not organisations or websites.
バージョンによって
PHP 8.2 to 8.5 account for 612,269 versioned hosts and are covered by the official release. PHP 5.x (368,570), 7.x (329,358) and 8.0–8.1 (185,789) are not; only some of the 7.x, 8.0 and 8.1 hosts can benefit from PHP’s source patches, if their operators build PHP themselves. PHP 5.6 and 7.2 alone represent about 371,000 hosts for which PHP publishes no fix at all.
国別
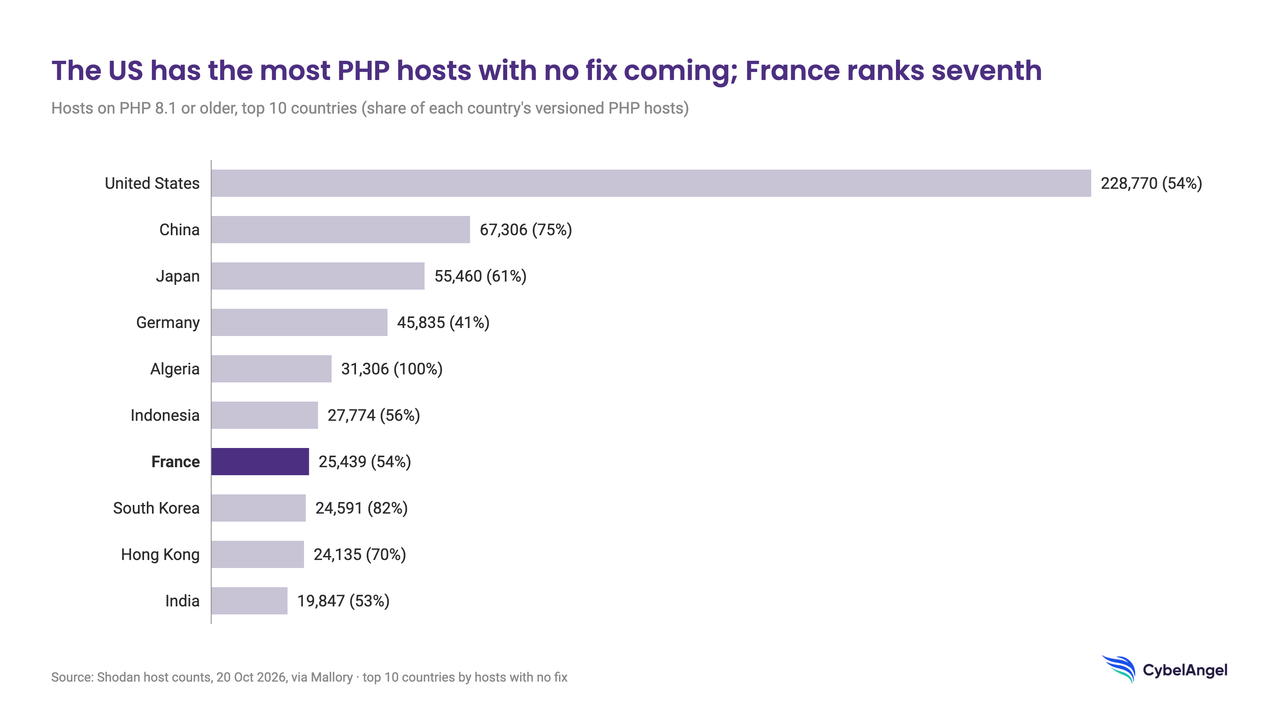
The United States has the largest number of hosts with no official release (228,770), followed by China, Japan and Germany. Among these ten countries, Algeria (100%, almost entirely PHP 5.3 on Telecom Algeria), South Korea (82%) and China (75%) have the highest shares. France counts 25,439 such hosts, 54% of its versioned PHP hosts.
ホストプロバイダーによって
Exposure is concentrated: Amazon (293,480 PHP hosts), Hostinger (142,401) and Alibaba Cloud (81,078) host the largest PHP populations, which makes provider-side patching decisive.
WordPress
~によると WordPress.org statistics reported by The Repository, 35.1% of WordPress sites run a PHP version the PHP project no longer supports, including 16.46% on PHP 7.4. Across the live Joomla and WordPress sites mySites.guru monitors, 22.7% run PHP 8.1 or older.
これらの数の限界
The real exposure is higher than banner counts suggest: about 740,000 PHP hosts hide their version, and shared hosting puts many websites behind one IP. Conversely, some Linux distributions (Debian, Ubuntu, RHEL) and LTS vendors backport fixes to older packages, so some hosts that report an old version may already be patched.
別の統計によると、フランスが1位だ。
Measuring active PHP services rather than hosts, Infrawatch observes about 11 million services across 4.38 million IP addresses, with France at 6.62 million, more than eight times the United States. Much of that concentration comes from Freebox OS, the management software of Free’s home routers; Infrawatch stresses this does not mean these hosts are exploitable.
スキャンした資産全体で確認したこと
After the release, CybelAngel scanned 1.3 million internet-facing assets. Among the sites that reveal their PHP version, 54% run an end-of-life branch.
推奨事項
The fix is out: patch PHP itself now; every other measure only buys time.
- Inventory every internet-facing PHP asset, including those run by hosting providers, agencies and appliance vendors, and record the branch and SAPI (PHP-FPM, mod_php, php-cgi).
- Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35, then restart PHP-FPM or the web server so the new interpreter is loaded. Check the version the site reports while serving a request, not
php -v, as the two binaries often differ. - On managed hosting, confirm with your host that the patch is applied, and take a fresh backup before anything changes on the server.
- Upgrade end-of-life branches (8.1 and older) to a supported version, or ask your distribution or LTS vendor for a backported fix. Until then, restrict access (VPN, IP allowlist) or isolate internet-facing applications, as CERT-EU recommends.
- Reduce exposure until you patch: take internet-facing PHP applications offline where you can.
- Check for compromise after patching, going back to at least June 2026: web shells, unexpected or modified PHP files, new admin users and unusual outbound connections. Watch for unexpected child processes of the web server, reduce the data and cloud privileges held by PHP servers, and check that logs are retained.
サイベルエンジェルがどのように支援しているか
Our teams are reviewing the external perimeters we monitor for the signals that matter here: exposed web servers, outdated software stacks and PHP-based control panels. Where we see heightened risk, we are reaching out to customers directly. If you are not a CybelAngel customer and want to understand your external exposure, contact our team.
Updated on 21 October 2026 after PHP’s security release. We will keep updating this article as exploitation data and vendor advisories emerge.
著者について