Lumma Stealer: Einblicke in die Malware-als-Service-Bedrohung
Inhaltsübersicht
Infostealers are a quiet but damaging threat. They slip onto a device, collect credentials, session cookies, and files, then pass them on for fraud or ransomware. LummaC2 Stealer is one of the most prolific, and one of the hardest to keep down.
Active since 2022, Lumma is sold as Malware-as-a-Service and spread mainly through social engineering. It survived a major international takedown in May 2025, a damaging leak of its alleged operators’ identities later that year, and still came back in 2026 with new loaders and a 64-bit variant. For businesses, the risk hasn’t gone away.
What is LummaC2 Stealer?
LummaC2, often shortened to Lumma, is an information-stealing malware written in C and first advertised on Russian-speaking cybercrime forums in 2022. It’s sold as Malware-as-a-Service (MaaS) to cybercriminals who want a ready-made way to collect sensitive data.
The malware targets web browsers, cryptocurrency wallets, and two-factor authentication (2FA) browser extensions, then sends the stolen data to its command-and-control (C2) servers.
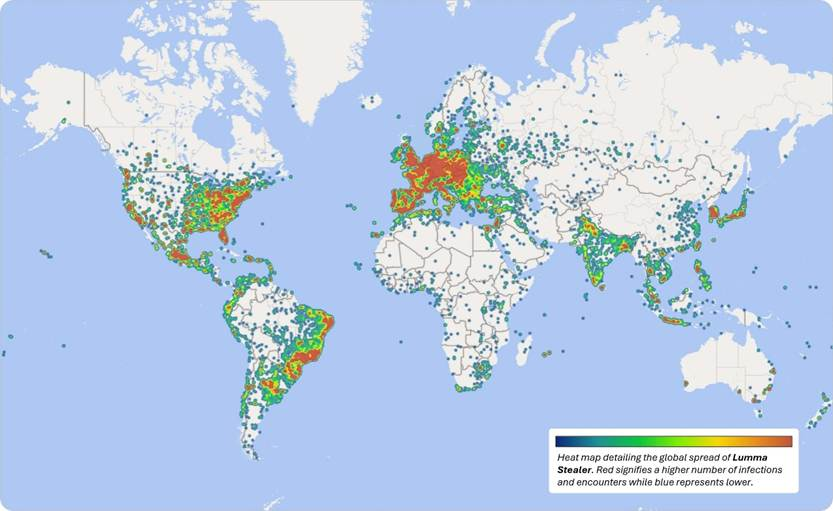
Its reach is significant. Between March 16 and May 16, 2025, Microsoft identified more than 394,000 Windows computers infected with Lumma worldwide.
In May 2025, Microsoft’s Digital Crimes Unit, the US Department of Justice (DOJ), Europol, and Japan’s Cybercrime Control Center (JC3) disrupted Lumma’s infrastructure. Within weeks, its operators had restored their infrastructure. That resilience is what makes Lumma a persistent threat for security teams.
Is Lumma Stealer still active in 2026?
Yes, although it no longer dominates the infostealer market the way it did before the takedown.
- Late 2025, a sharp decline: A doxxing campaign exposed alleged core members of the operation and severely disrupted its operations. ANY.RUN recorded a 65% drop in Lumma detections in Q4 2025, and many customers moved to rival stealers such as Vidar, which has led major infostealer trackers since.
- December 2025 – January 2026, a resurgence: Bitdefender reported that Lumma operations scaled significantly, delivered through the CastleLoader malware loader and increasingly through ClickFix lures.
- February 2026, new variants: Microsoft Threat Intelligence disclosed a ClickFix variant that tells victims to open Windows Terminal instead of the Run dialog. The same month, Gen Digital observed the first campaigns of Remus, a 64-bit variant of Lumma with new anti-analysis checks and more resilient C2 infrastructure.
The pattern is familiar: disruption slows Lumma down, but its code, affiliates, and distribution networks keep resurfacing in new forms.
How Lumma Stealer infects victims
Lumma doesn’t rely on a single delivery method. Its affiliates use several initial access vectors to keep new infections coming.
- Phishing emails: Messages with malicious HTML attachments or links that lead to fake download or verification pages.
- Malvertising: Malicious ads and poisoned search results that distribute loaders, cracked software, or fake installers.
- Fake repositories and downloads: GitHub, file-sharing sites, and torrents seeded with bogus tools such as game cheats, key generators, pirated software, or “free” utilities.
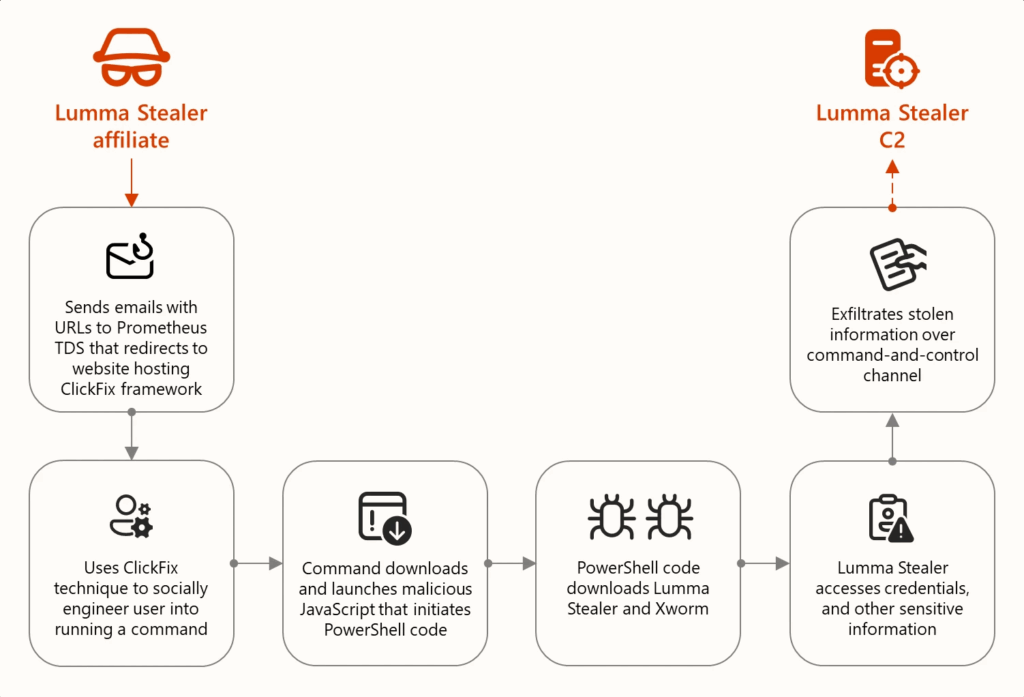
- Fake CAPTCHA pages (ClickFix): Compromised or malicious websites show a fake CAPTCHA that asks the user to “verify” by pasting a command into the Run dialog or, in newer variants, Windows Terminal. The command silently downloads and runs a loader such as CastleLoader, which then installs Lumma.
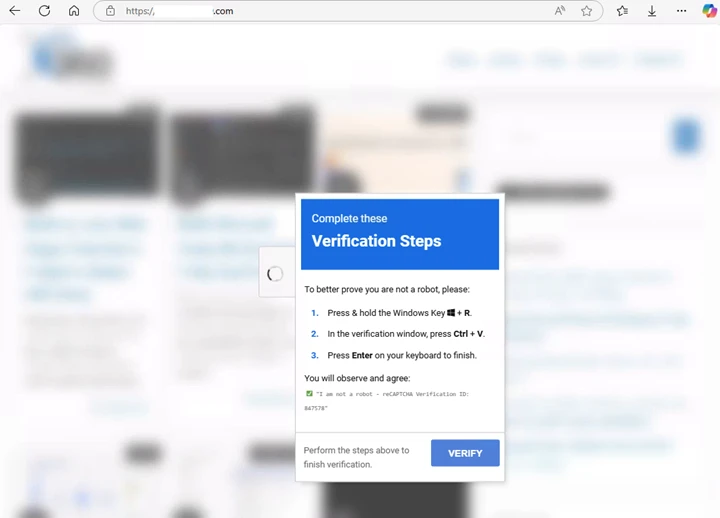
Every method shares one thing: social engineering. By disguising Malware as something helpful or urgent, threat actors exploit human trust rather than breaking through hardened defenses. Once launched, Lumma starts collecting and exfiltrating data immediately.
What information Lumma targets
Once installed, Lumma casts a wide net. Its modules collect information that can be sold, reused for fraud, or used to launch further intrusions.
- Web browsers: Saved credentials, session cookies, autofill data, and browsing history from Chrome, Edge, Firefox, and other major browsers.
- Cryptocurrency wallets and 2FA extensions: Wallet files and data from authenticator browser extensions, putting digital assets and MFA-protected accounts at risk.
- VPN clients and productivity apps: Session tokens and configuration files from VPN tools, Telegram, and email clients.
- Clipboard monitoring: Watches the clipboard and swaps cryptocurrency wallet addresses for attacker-controlled ones.
- Screenshots and system data: Desktop screenshots, system specifications, and IP addresses that give attackers context for further exploitation.
Each data point has value. Credentials feed account takeover campaigns, system profiles help attackers tailor ransomware or fraud, and session cookies are especially dangerous. A stolen session cookie lets an attacker replay an already-authenticated session, so MFA alone doesn’t stop it: the attacker never needs the password or the second factor.
Evasion and anti-analysis techniques
Lumma’s developers invest heavily in staying hidden. The malware is built to frustrate static and dynamic analysis, change frequently, and blend its C2 traffic into legitimate services.
- Obfuscated code: Lumma’s internals are deliberately scrambled, making it harder for analysts and antivirus tools to understand what it does.
- Frequent updates: New builds appear regularly, each adjusted to slip past security tools. The Remus variant added further anti-analysis checks in 2026.
- Sandbox awareness: The malware can detect when it’s running in a virtual machine or sandbox and stop executing to avoid analysis.
- Multi-stage delivery: Lumma is usually fetched by a loader or a malicious HTML/HTA file that triggers PowerShell to download and run the payload. Some campaigns use DLL sideloading through signed binaries, or scheduled tasks for persistence.
- Hidden C2 addresses: Rather than hardcoding every server, Lumma looks up its current C2 addresses from “dead drop” locations such as Steam profiles and Telegram channels, and Remus uses Ethereum smart contracts. Its infrastructure rotates often, which makes it hard to block for long.
Together, these techniques make Lumma hard to detect. Obfuscation hides its code, sandbox checks block analysis, and fast-rotating C2 infrastructure means indicators of compromise expire quickly.
That’s why defenders need behavior-based detection on endpoints and continuous external threat intelligence to spot new infrastructure and exposed data early.
Command-and-control infrastructure
Lumma doesn’t depend on a single server. Its C2 is layered: some domains are built into the Malware, and fallback mechanisms let it find new ones if those are blocked.
In many builds, Lumma checks Steam profile pages and Telegram channels, where operators post encoded C2 addresses. Because this traffic goes to legitimate, widely used platforms, it’s hard to block without disrupting normal business use. Lumma has also abused services such as Cloudflare to hide its servers, and in February 2025 it was observed bypassing Cloudflare’s warning pages. The Remus variant goes further, replacing Steam and Telegram with Ethereum smart contracts, a technique known as EtherHiding.
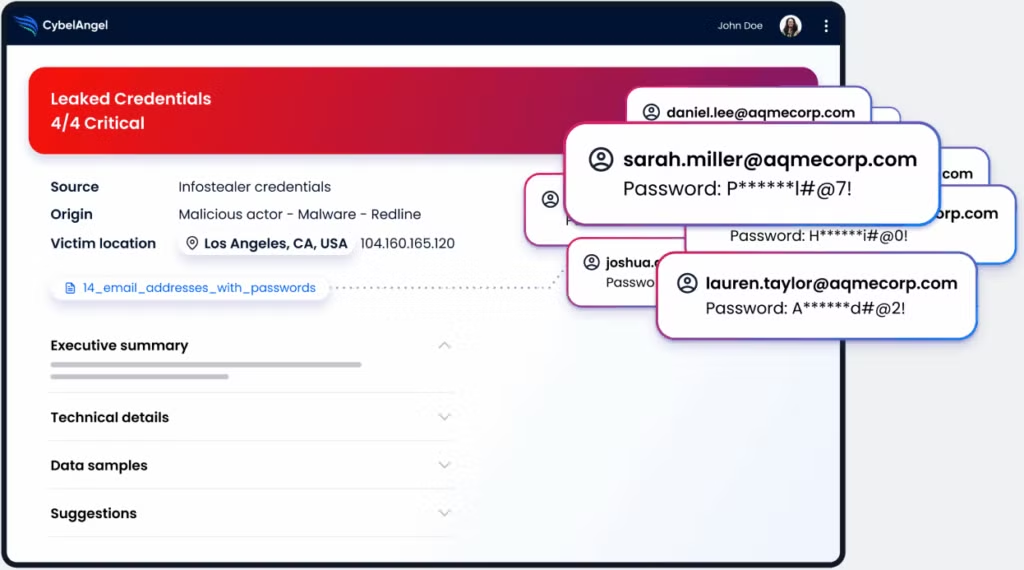
This layered design explains why takedowns have only a temporary effect. In May 2025, Microsoft’s Digital Crimes Unit seized or blocked approximately 2,300 malicious domains, and more than 1,300 were redirected to Microsoft sinkholes. At the same time, the DOJ seized Lumma’s central control panel and the marketplaces where it was sold. Within weeks, new Lumma infrastructure was online and campaigns had resumed.
From stolen data to real-world threats
Stolen data is just the beginning. Once credentials and cookies are exfiltrated, they’re packaged into “logs” and sold on dark web marketplaces or shared directly with other cybercriminals. This fuels a market where access to corporate accounts is traded like a commodity.
From there, the risks escalate. Initial access brokers and ransomware groups buy stolen logins to break into corporate networks. Fraud groups use them to hijack accounts or drain cryptocurrency wallets.
Consider a simple chain. An employee lands on a fake CAPTCHA page and pastes a command that runs a PowerShell script. Lumma installs and steals the employee’s saved VPN credentials and active session cookies.
Days later, attackers log in, escalate privileges, and explore the network. Sensitive files are copied out, backups deleted, and ransomware deployed. What started as “just an infostealer” ends as a full-scale breach.
That’s why CISOs can’t dismiss Lumma or its peers. Every credential theft is a potential entry point, and without early detection, it can escalate quickly.
Detecting and defending against Lumma
Spotting Lumma requires both endpoint visibility and external intelligence. Static indicators fade fast, so defenders need layered methods.
1. Detection methods
- Suspicious process chains: Alert on Explorer launching PowerShell, Windows Terminal, or mshta with encoded or download commands, a strong sign of ClickFix.
- Unusual persistence: Watch for new scheduled tasks and executables or DLLs dropped in folders such as
C:\ProgramDataor user AppData directories. - Abnormal access to browser data: Flag non-browser processes reading browser credential and cookie stores or wallet files.
- Odd network traffic: Look for unexpected processes contacting Steam profiles, Telegram, or blockchain endpoints, followed by outbound uploads.
- IOC hunting and sandboxing: Track domains, IPs, and hashes from recent campaigns, and detonate suspicious files in a sandbox, keeping in mind that Lumma may detect it.
2. Defensive measures
- Train users on ClickFix: Make clear that no legitimate website will ever ask them to paste a command into Run, PowerShell, or Windows Terminal.
- Restrict scripting: Limit PowerShell, mshta, and the Run dialog for standard users where possible, and use application control to block unapproved executables.
- Protect sessions, not just passwords: Phishing-resistant MFA, such as FIDO security keys, protects the login itself, but not a stolen session. Shorten session lifetimes, use conditional access and device-bound tokens where available, and revoke active sessions immediately after an infection.
- Stop storing passwords in browsers: Use an enterprise password manager instead, and audit browser extensions, especially authenticator and wallet plugins.
- Block malvertising and pirated software: Use secure browsing controls and ad filtering, and prevent software installation from untrusted sources.
- Monitor for exposed credentials externally: Infostealer logs often appear on underground markets before attackers use them. Detecting them early gives you time to reset credentials and revoke sessions.
CybelAngel supports this last step. Credential Intelligence identifies compromised credentials linked to your domains, and Überwachung des Dark Web tracks mentions of your organization on underground forums and marketplaces, so your team can act before attackers use the stolen data.
FAQs
Yes. After the May 2025 takedown and a decline in late 2025, Lumma resurged in early 2026 through CastleLoader and ClickFix campaigns, and a 64-bit variant called Remus appeared in February 2026.
An infostealer is malware designed to quietly collect sensitive information from an infected device, such as passwords, session cookies, or wallet keys, and send it back to attackers.
Once executed, infostealers run quietly in the background. They scan browsers, apps, and files for stored credentials, cookies, or wallet data, then exfiltrate it to attacker-controlled servers. Some also capture screenshots or monitor the clipboard.
Mostly through social engineering: phishing emails, malicious ads (malvertising), fake software downloads, and fake CAPTCHA pages that trick users into running a command themselves.
Not entirely. MFA protects the login, but Lumma steals session cookies created after login. An attacker can replay those cookies to access accounts without the password or second factor. Revoking sessions after an infection is essential.
Wallets store private keys that give direct access to digital assets. Stealing them lets attackers transfer funds quickly, and blockchain transfers are very hard to reverse.
MaaS is a business model where cybercriminals rent out malware and its infrastructure to other attackers, usually through subscriptions. It lowers the barrier to entry, letting even low-skill actors run campaigns.
Detection relies on monitoring for suspicious PowerShell or Windows Terminal activity, unusual scheduled tasks, and access to browser data stores, alongside IOC hunting and sandboxing. To respond, isolate the endpoint, reimage it, reset every credential stored on it, and revoke all active sessions and tokens for the affected user.
Stolen logins and session cookies often lead directly to account takeover, ransomware, or data breaches. A single set of compromised credentials can open the door to a wider compromise.
Schlussfolgerung
Lumma shows how quickly infostealer operations adapt. A takedown, a public exposure of its alleged operators, and a market shift toward rivals all slowed it down, but new loaders, lures, and variants kept it in circulation.
CybelAngel helps you close the gap between infection and exploitation. By identifying credentials exposed by Lumma and other infostealers early, we give your team the chance to reset accounts and revoke sessions before stolen data turns into a breach.
Über den Autor